August 17, 2026 by sig9
Hacker Wars - August 17, 2026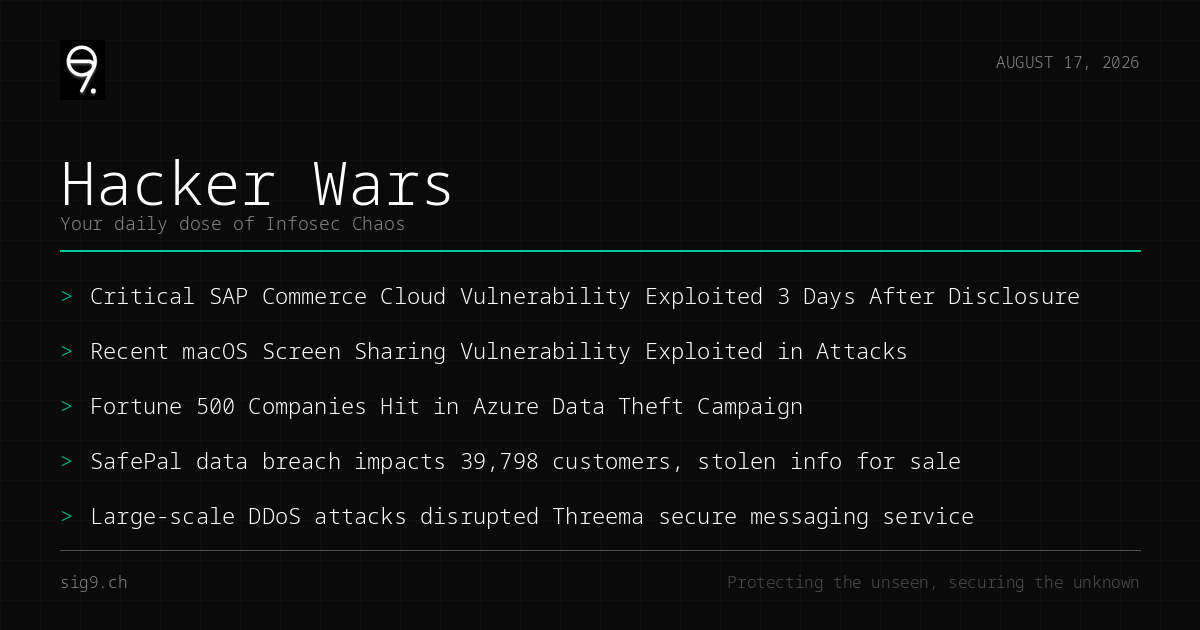
Your daily dose of infosec chaos
The window between disclosure and exploitation keeps shrinking, and SAP Commerce Cloud got popped just three days after its advisory went live. macOS collects another in-the-wild exploit, someone claims to be auctioning off Fortune 500 data from Azure, a hardware wallet vendor leaked its customer list, and Switzerland’s own Threema spent days absorbing DDoS fire. Settle in.
SAP Commerce Cloud Popped Three Days After Disclosure
Attackers are exploiting CVE-2026-58231, a critical flaw allowing arbitrary code execution and compromise of internal components in SAP Commerce Cloud, a mere three days after it was disclosed. Your emergency patch SLA is now officially slower than the attackers.
What to do: Patch SAP Commerce Cloud instances now and audit internet-facing deployments for signs of post-exploitation.
macOS Screen Sharing Bug Hands Attackers Root And A Miner
Threat actors exploited a recent macOS Screen Sharing vulnerability to gain root on unpatched Macs and deploy a Monero cryptominer. The payload may be pocket change, but the root access it rode in on is very much not.
What to do: Update macOS across the fleet and alert on unexplained CPU spikes or unknown mining processes.
Fortune 500 Data Allegedly Siphoned From Azure
A threat actor claims to have exfiltrated millions of records belonging to McDonald’s, TCS, Vodafone, and other large organizations from Azure. Breach claims this grandiose often shrink under scrutiny, but with these names attached, nobody should be complacent.
What to do: Review Azure sign-in logs and third-party service principal activity, and prune partner access nobody owns.
SafePal Breach Puts 40,000 Crypto Customers Up For Sale
Hardware wallet maker SafePal says a flaw was abused to steal order information on roughly 39,800 customers, and the data is already being flogged by a threat actor. Cold wallets protect your keys, not the e-commerce database documenting exactly who holds them.
What to do: If you ordered from SafePal, assume targeted phishing is coming, and never, ever share a recovery phrase.
Threema Knocked Sideways By Sustained DDoS Onslaught
Multiple large-scale DDoS attacks disrupted Threema’s secure messaging service earlier this week, degrading communications for its users. End-to-end encryption is cold comfort when the servers on the other end are drowning in junk traffic.
What to do: Define a fallback communication channel before your primary one has a very bad day.
Until next time, keep your systems patched and your credentials rotated.
Brought to you by sig9 - sig9.ch | Protecting the unseen, securing the unknown
This bulletin is provided for informational purposes. Contact us for tailored security analysis.